
Protect your business.
Automatically.
AI monitoring, vulnerability scanning, and compliance — enterprise-grade security without the enterprise price tag.
9+
scanners
33
integrations
0
agents needed
Full platform walkthrough — 9 security features in 2 minutes
Platform
Everything in one place.
Six security domains. One dashboard. No agents required.
Asset Management
Discover and track domains, servers, cloud resources, and SaaS tools automatically. Real-time risk scoring surfaces your highest-priority exposures first.


What we discover
DNS · TLS · WHOIS
EC2 · S3 · RDS · VMs
Okta · GWS · M365
GitHub · GitLab
Linux · macOS · Win
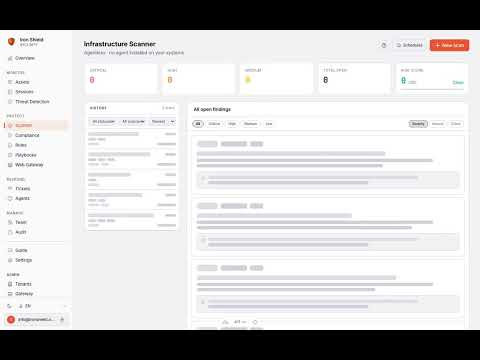
Agentless Scanner
No software to install. Connect your cloud accounts, SaaS tools, and code repositories — Iron Shield scans for misconfigurations, exposed credentials, CVEs, and compliance gaps automatically.
30+ integrations — AWS, GCP, Azure, GWS, M365, GitHub, Okta, and more
Scans complete in under 30 seconds with zero impact on production
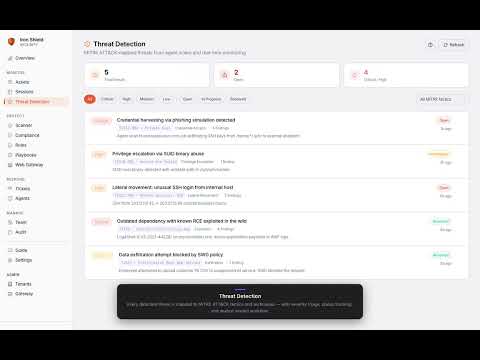
Every finding mapped to MITRE ATT&CK and remediation steps included
Agentless — read-only API access, no credentials stored on your infra
On-prem Agent
~15 MB
RAM idle
<1%
CPU idle
~8 MB
Disk
AI Governance Extension
Chrome MV3 extension that intercepts AI API traffic in the browser — redacts PII before prompts leave the device and logs every interaction for audit.
Chrome Web Store · MV3 · Enterprise-ready
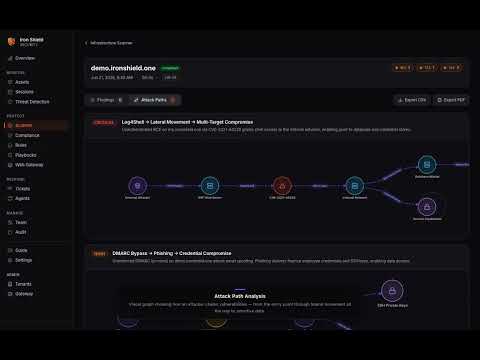
Attack Path Analysis
Iron Shield connects individual findings into end-to-end attack chains — showing how an exposed credential leads to lateral movement, privilege escalation, and data exfiltration.
Exposed API key
Initial AccessIAM role assumption
Priv. EscalationS3 enumeration
DiscoveryData exfiltration
ExfiltrationMITRE ATT&CK · Graph-based · Auto-correlated
Rule Engine
Write security policies in plain GRL — no coding required. Forward chaining enforces real-time access rules, stream rules detect suspicious patterns, and backward chaining traces compliance proof trees. Rules hot-reload instantly with zero downtime.
< 5ms decisions
Compliance
Backward-chaining proof trees evaluate each control against your GRL rules. Per-control re-check, evidence trace, and CSV export for auditors.
Deepfake Detection
Synthetic voice & video in Slack, Zoom, Teams
Prompt Injection Shield
Block jailbreaks and data disclosure in real time
Incident Playbooks
Step-by-step runbooks for non-security staff
Jira & Trello Tickets
Create tickets from findings in one click, track them on the Tickets page
Product demos
See Iron Shield in action
15 videos covering every scanner, the rule engine, agents, and the Chrome Extension.
Getting started
Up and running in minutes.
Connect your infrastructure
Add domains, cloud accounts, and SaaS integrations. Iron Shield discovers assets automatically via API.
Run your first scan
Select scan targets and scanner types. Severity-ranked findings with remediation guidance appear in seconds.
Define your policies
Write security rules using the GRL rule engine. Policy violations trigger alerts and audit log entries.
Monitor continuously
Schedule daily scans, track posture trends over time, and export compliance reports for stakeholders.
Ready to get started?
Sign in to your Iron Shield dashboard or contact your administrator to request access.
Open Iron Shield